Service accounts and keys get an owner
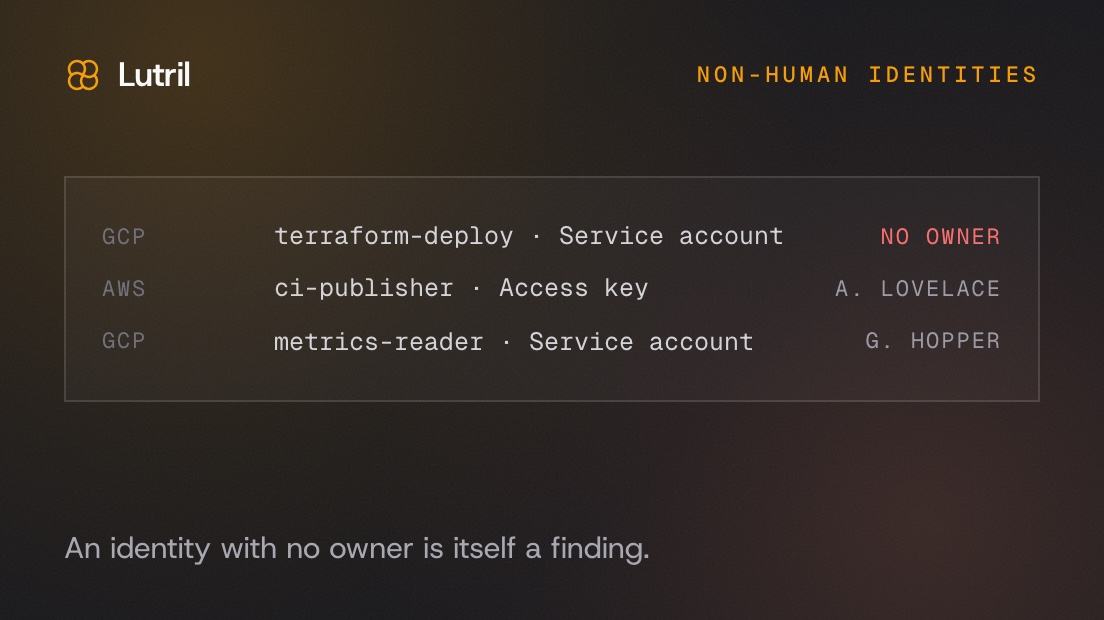
Every cloud estate accumulates service accounts, access keys and tokens that no joiner-mover-leaver process ever touches. They outlive the project that created them and the person who created it, and an identity provider has no opinion about any of them, because none of them is a person.
They now have a surface of their own. Collectors pull them from AWS and Google Cloud, each one is tiered by risk, and the secrets attached to a project are listed alongside it. The part that changes behaviour is the owner: an identity with a named owner is one somebody can be asked about at review time, and an identity without one is itself a finding.
Adding a provider is a contract rather than a special case. A collector exports its provider name and a collect function returning normalised records, and registers itself. GitHub is the next container in the same shape.