The browser extension finds the apps OAuth cannot see
OAuth discovery is the cheapest shadow IT signal there is, and it has a blind spot you cannot close from the server side. An application somebody signed up for with their work email and a password never touches your identity provider, so nothing you can query knows it exists.
The extension closes it from the browser, under a privacy model that is the point rather than a footnote. It transmits a hostname only when that domain is already in the SaaS catalogue, matched on the device, so general browsing never leaves the machine. It sends hostnames and never full URLs, paths or query strings, and it watches the main frame only, so iframes and ads are not in scope.
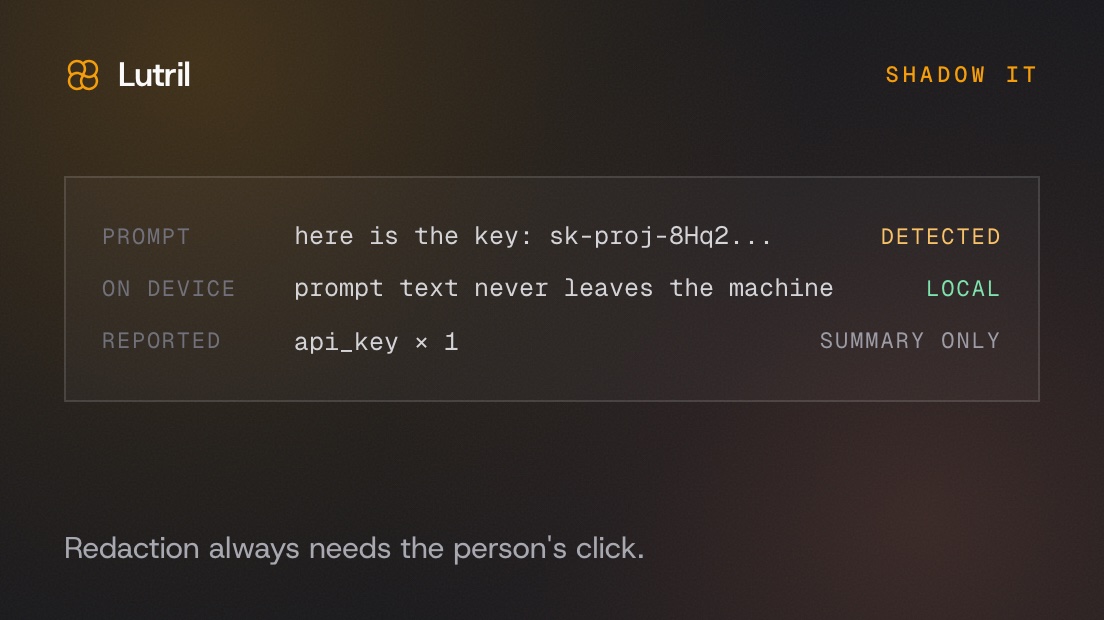
On ChatGPT, Claude and Gemini it also scans the prompt before it is sent, on the device, for emails, card numbers, IBANs, JWTs and shaped API keys. When it finds something it offers to redact it in place. Detection is entirely local, the prompt text never leaves the machine, only a type and count summary is reported, and the redaction always needs the person's click. The extension never silently rewrites what somebody typed.