Integrations
Lovable, Vercel and Claude Enterprise
Three new integrations, each governed for exactly what its API allows and nothing more.
Read the detailNew integrations, governance changes and fixes, newest first. Written for the people who use Lutril, not for a release note.
Three new integrations, each governed for exactly what its API allows and nothing more.
Read the detail
Slack deactivation, Figma seats, Notion and Keycloak expose nothing for removing an access. Save a service account once and Lutril uses it for the account writes an OAuth token cannot make.
Read the detail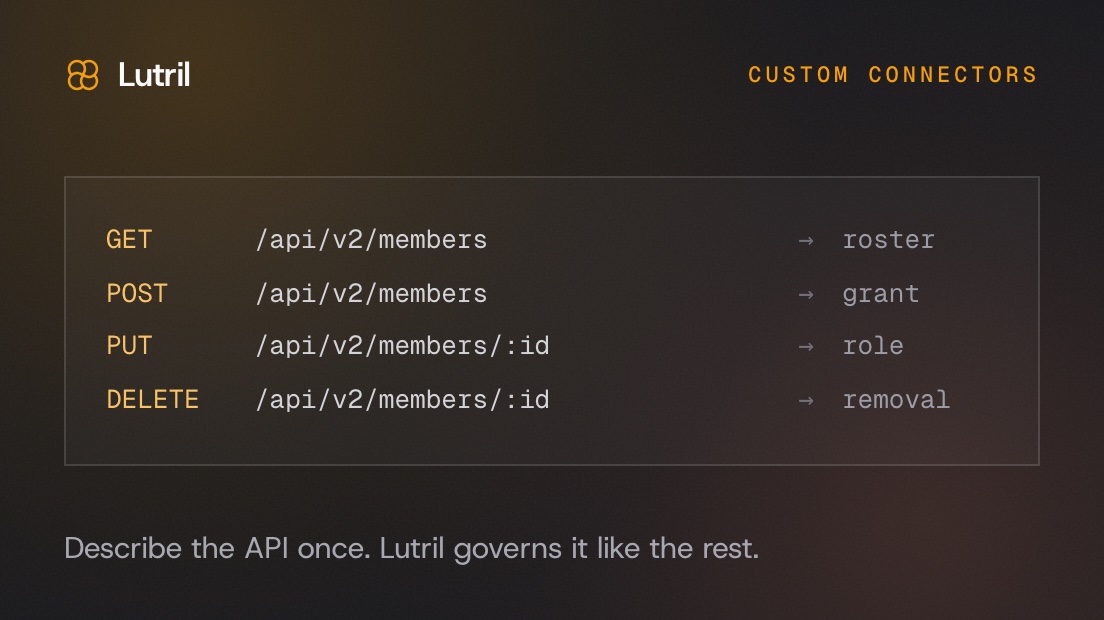
Describe an HTTP or GraphQL admin API in a connector spec, and Lutril governs that application like any other: roster, access reviews, grants and removals.
Read the detail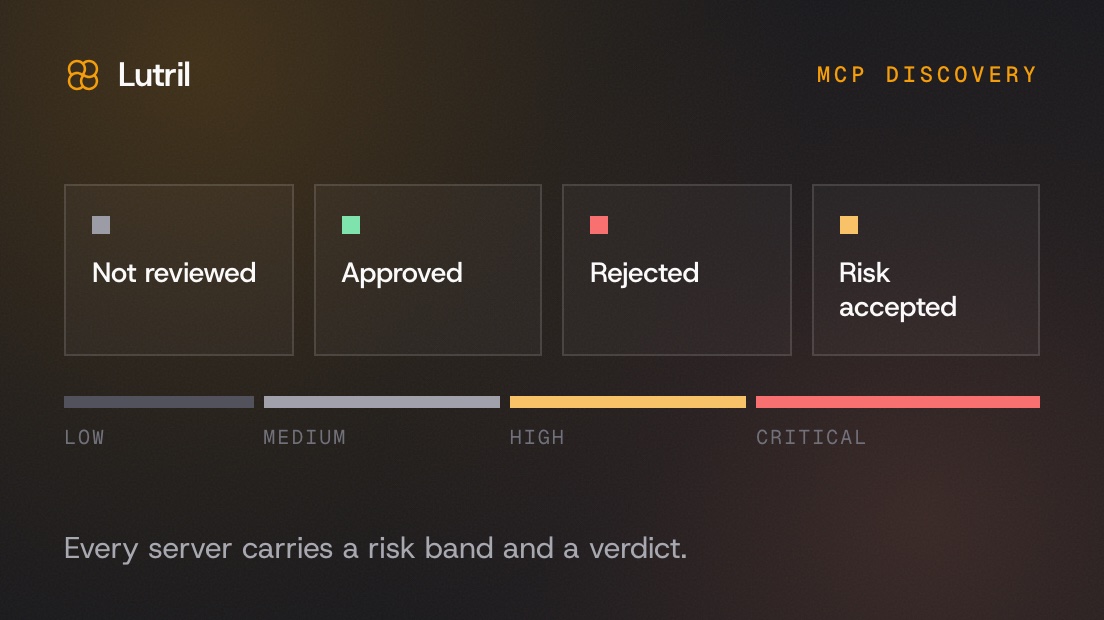
The discovery screens were rebuilt around the verdict rather than the inventory. Every server carries its risk band and its review state.
Read the detail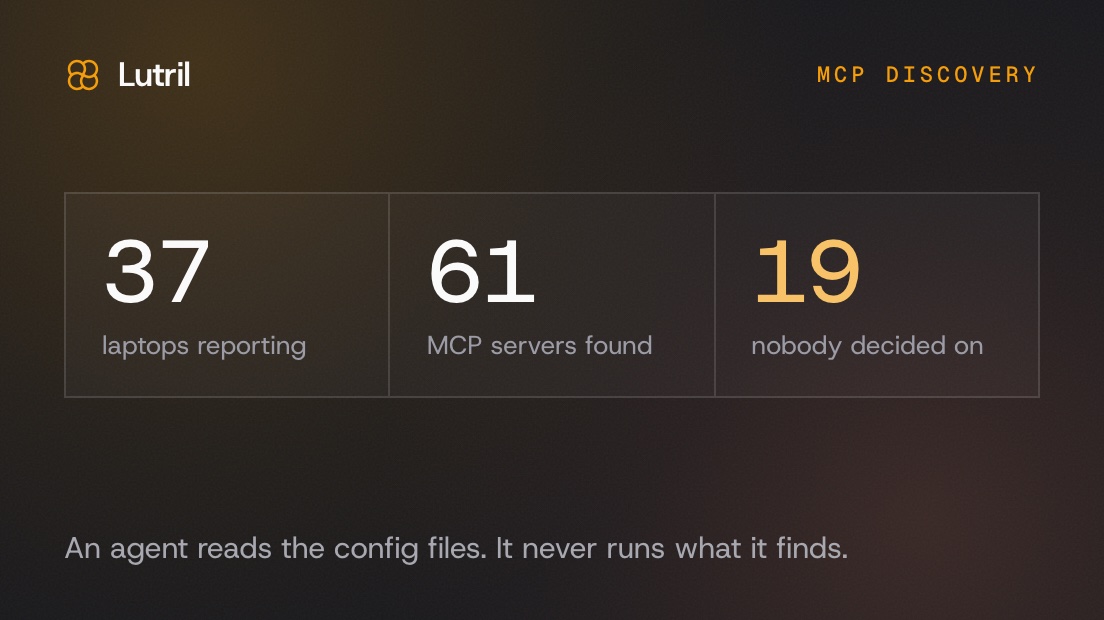
A read only agent, deployed by MDM, reads the config files of the 17 MCP clients on every laptop. It never runs what it finds.
Read the detail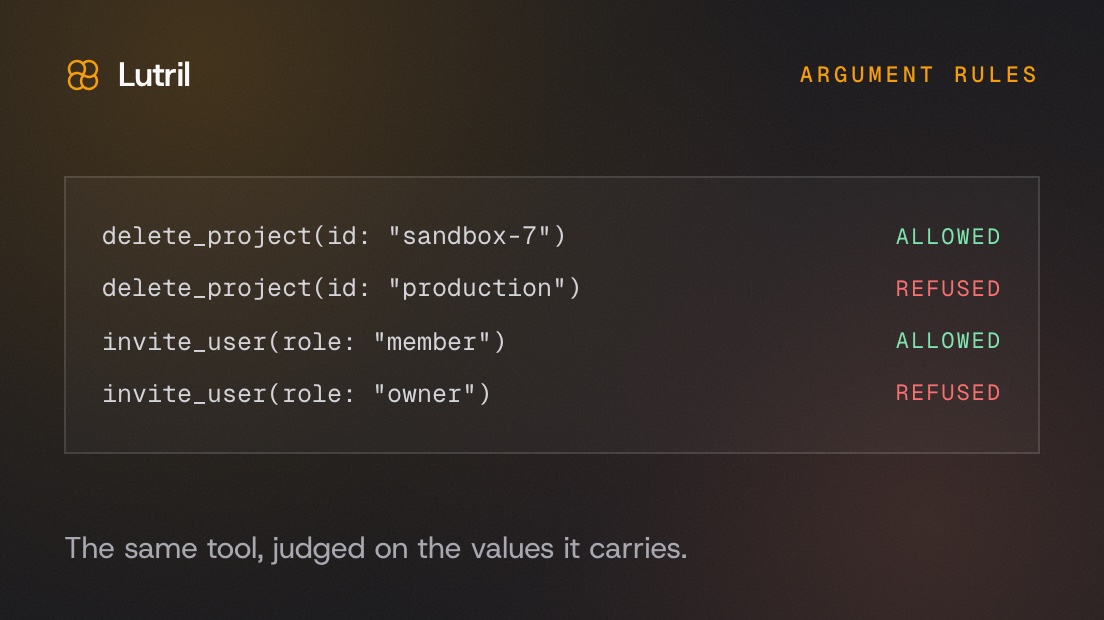
The gateway already decided who may call which tool on which server. It now decides with what values.
Read the detail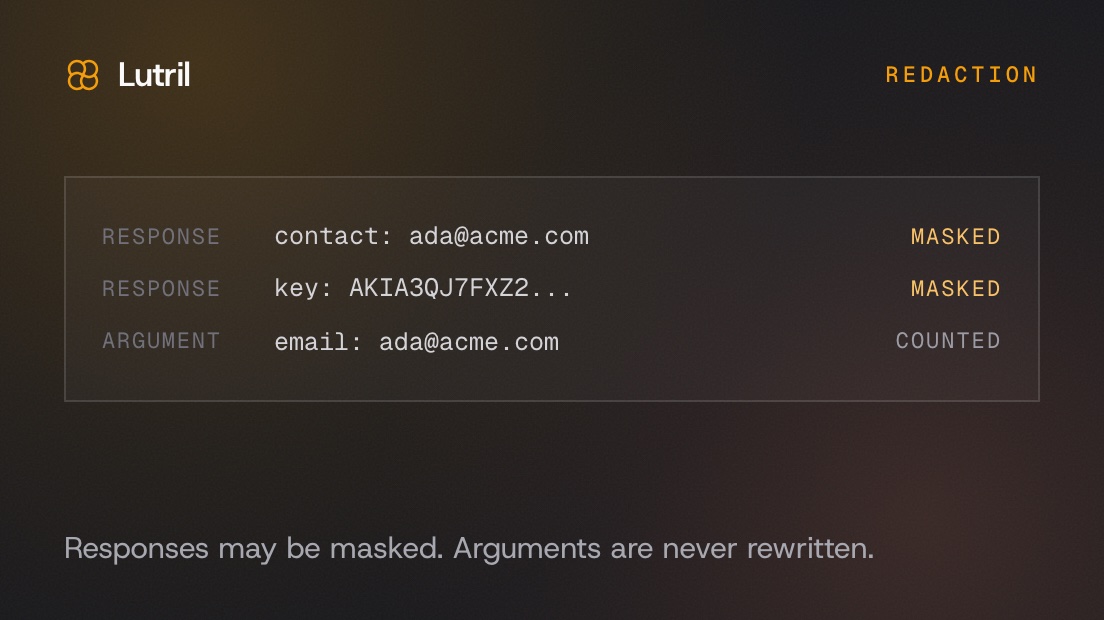
Nothing read the payloads crossing the MCP path before. A vendor response carrying a customer's email no longer goes into a third-party model's context unexamined.
Read the detail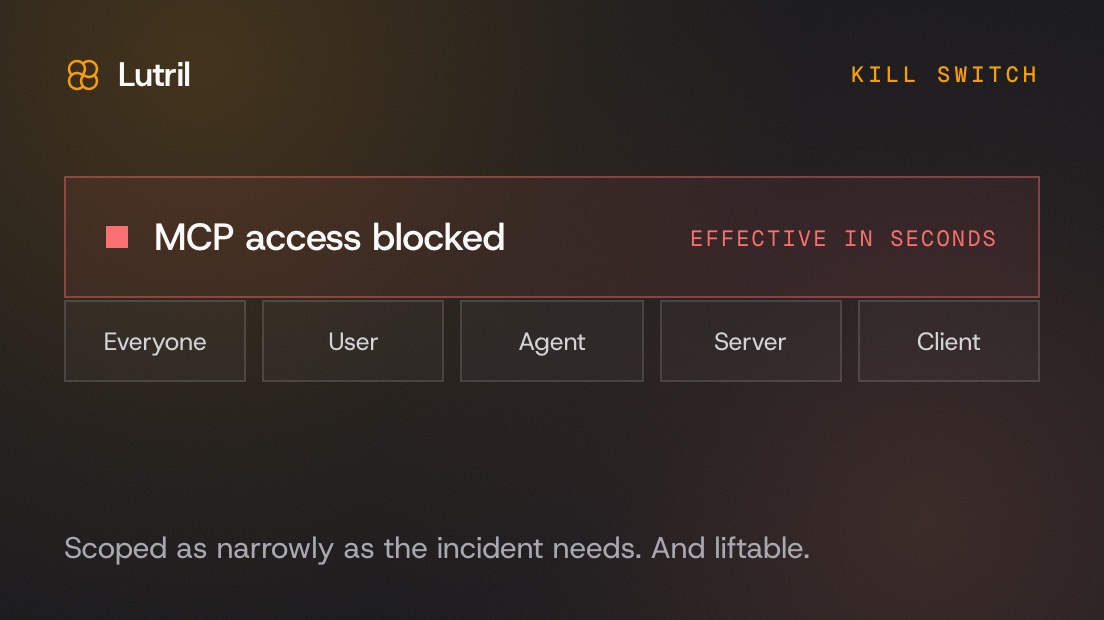
MCP access tokens are stateless, so until now there was no way to stop one before it expired. A block refuses every token and refuses to mint new ones.
Read the detail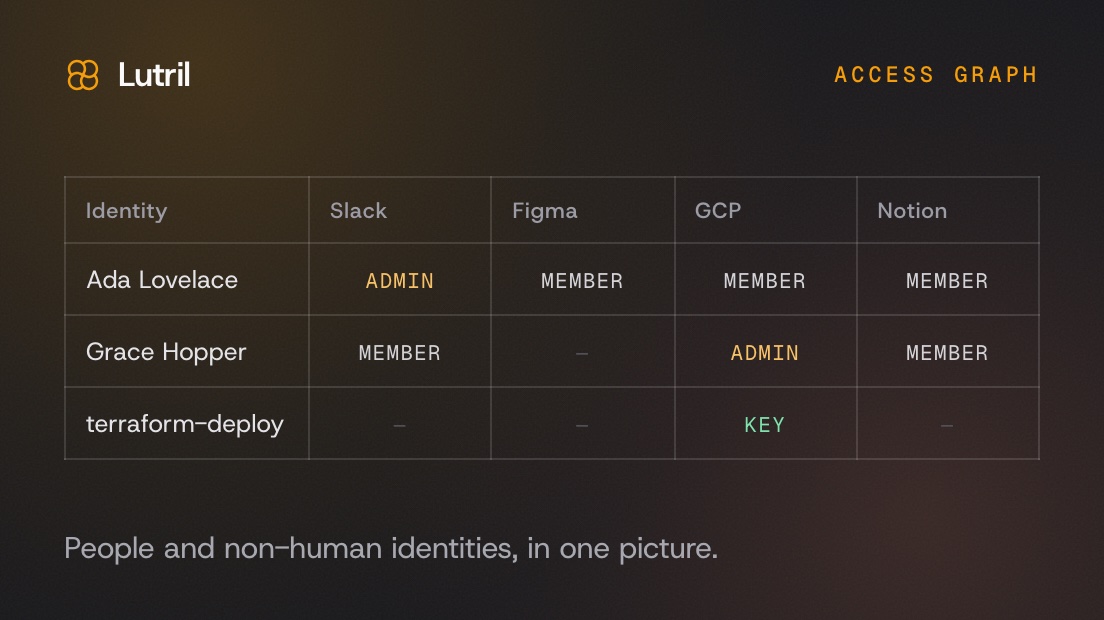
A people by applications matrix, with a graph view beside it, covering human and non-human identities together.
Read the detail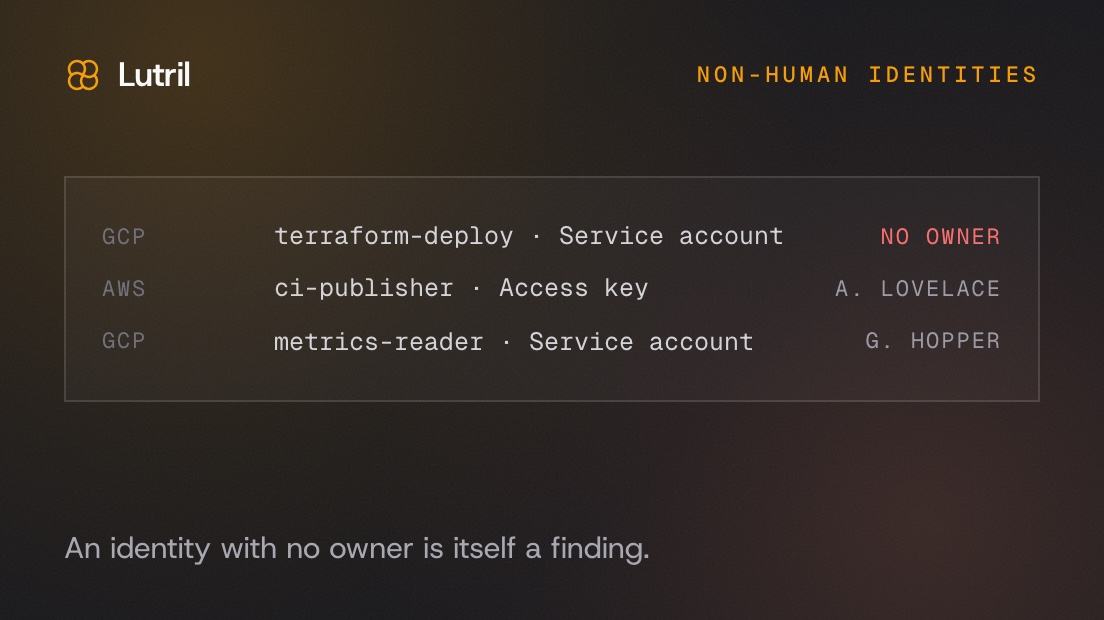
Non-human identities now have their own surface: collected from AWS and Google Cloud, tiered by risk, and each one answerable to a named person.
Read the detail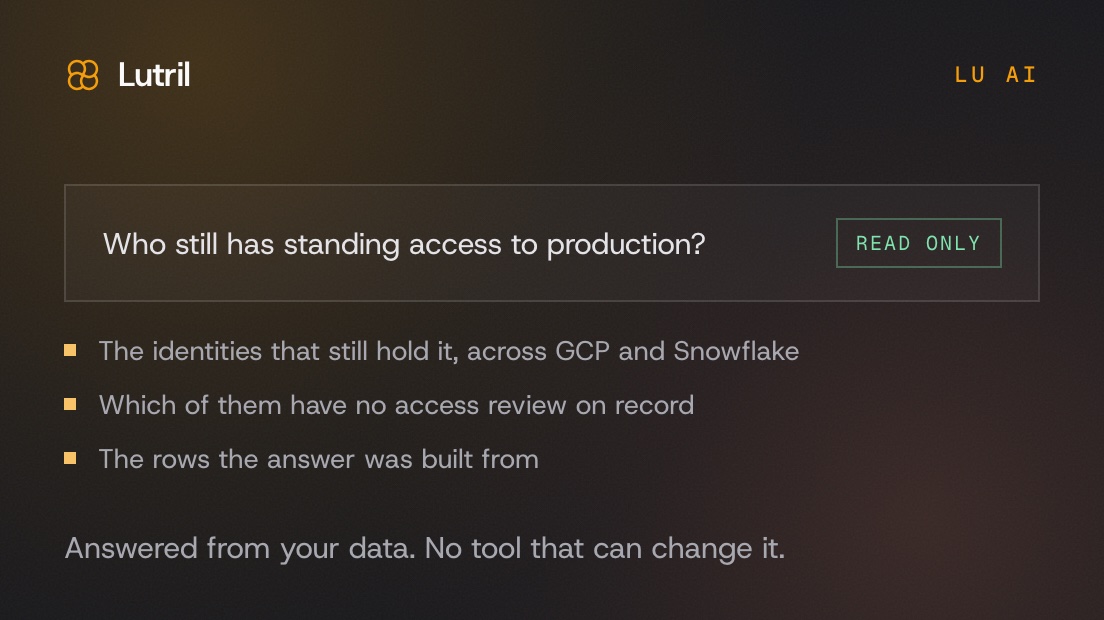
Ask who still has standing access, or which agents nobody owns, and get an answer from this tenant's real governance data rather than from documentation.
Read the detail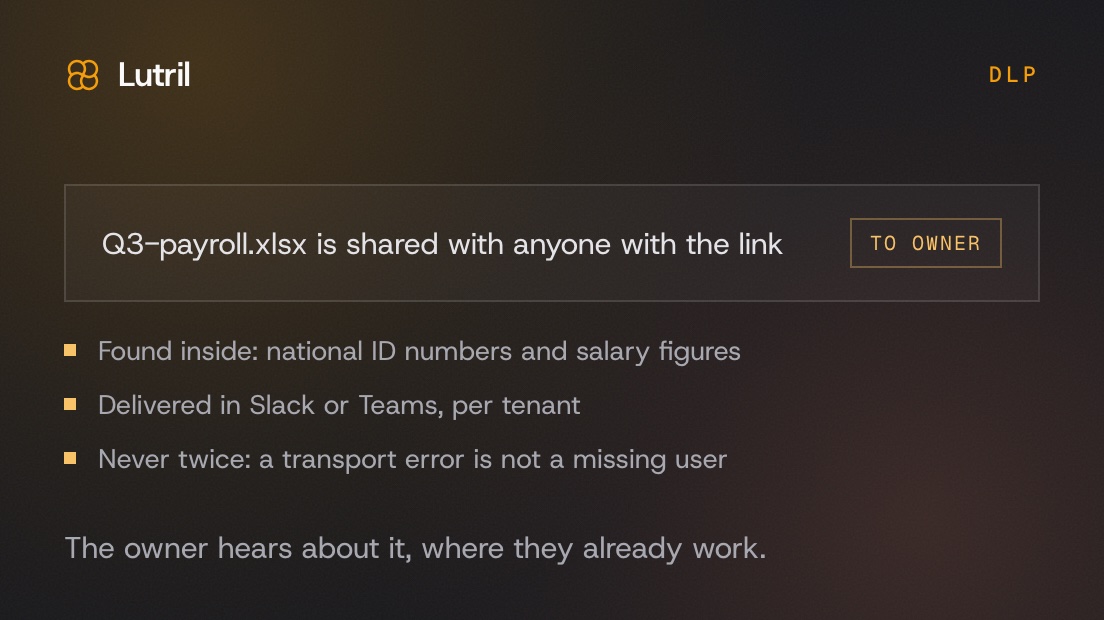
Shared files are classified and the owner hears about it where they already work, in Slack or in Teams, according to the tenant rather than the file's provider.
Read the detail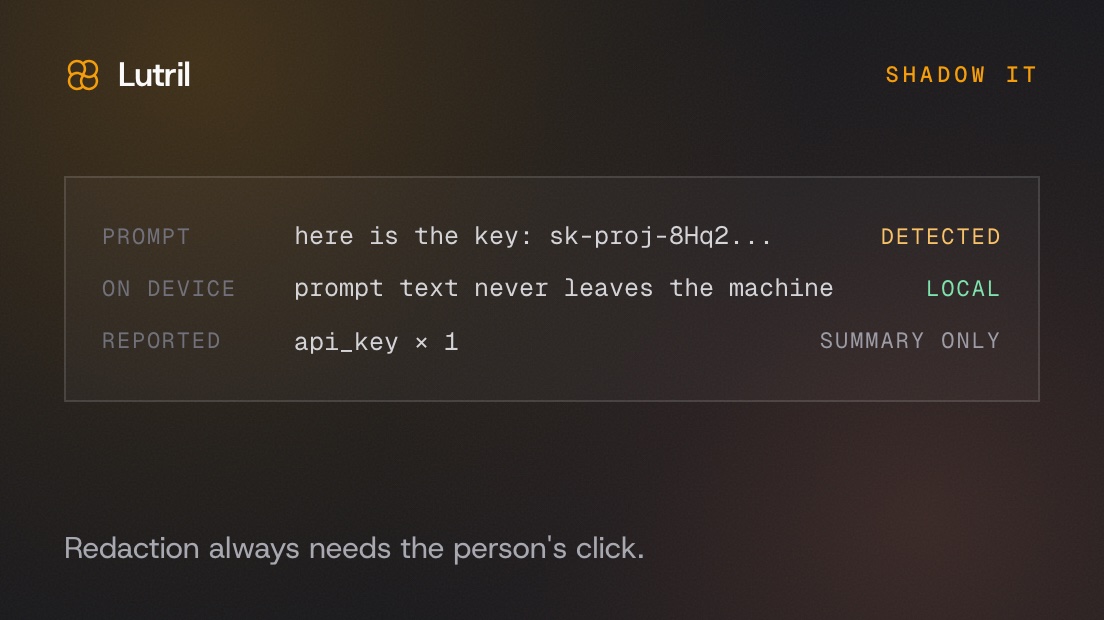
OAuth discovery surfaces every app somebody authorised with Google or Microsoft. It cannot see the ones they signed up for with a work email and a password.
Read the detail